Betterleaks Launches as a New Open-Source Tool for Detecting Leaked Secrets
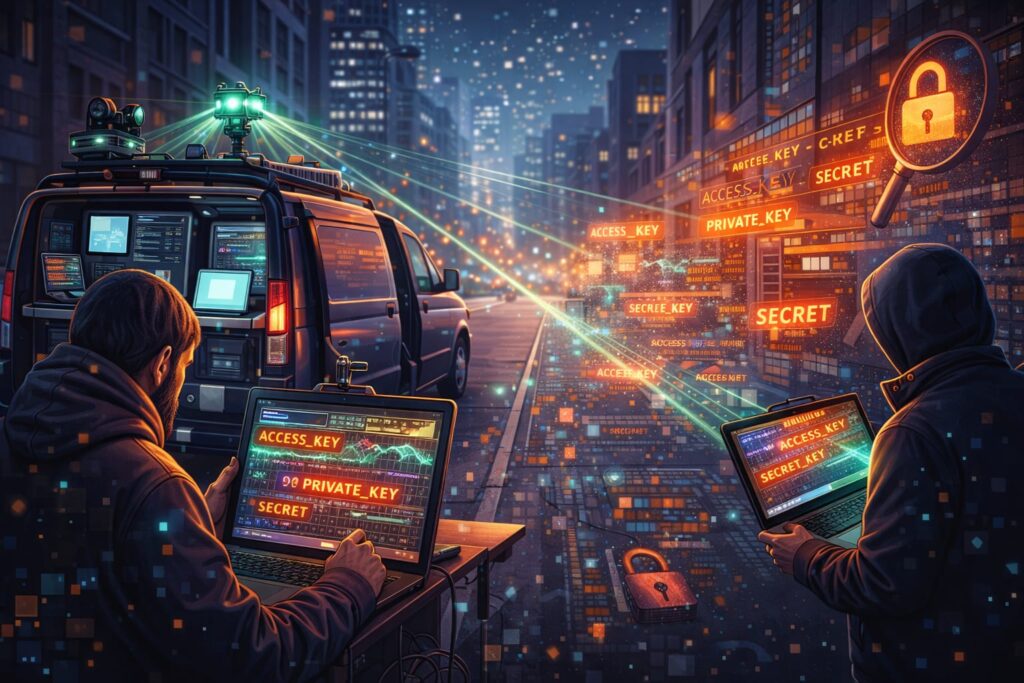
A new open-source security tool called Betterleaks has been released to help developers identify sensitive information accidentally exposed in source code. The tool is designed to scan files, directories, and Git repositories to detect leaked credentials such as API keys, tokens, and passwords before they can be abused.
Secret leaks remain one of the most common security risks in modern software development. Tools like Betterleaks aim to reduce that risk by automatically analyzing repositories and alerting developers when sensitive data is detected.
What Is Betterleaks?
Betterleaks is a secret-scanning tool built to detect exposed credentials in source code repositories. Developers sometimes unintentionally include configuration files, environment variables, or authentication tokens in their code during development.
If these secrets are pushed to public repositories or shared environments, attackers can quickly discover them and use them to gain unauthorized access to services or infrastructure.
Betterleaks scans project files and repository history to identify:
- API keys
- Authentication tokens
- Database credentials
- Private keys
- Cloud service access tokens
By detecting these secrets early, developers can remove them and rotate credentials before they are exploited.
Why Secret Detection Matters
In many modern development workflows, code is constantly pushed to version control systems and shared across teams. While this speeds up collaboration, it also increases the chance that sensitive information may accidentally appear in the repository.
Attackers often scan public repositories looking for exposed secrets. Once discovered, those credentials can be used to access databases, cloud accounts, internal APIs, or other critical systems.
Secret scanning tools like Betterleaks help organizations:
- Identify leaked credentials before deployment
- Improve the security of development pipelines
- Detect secrets in historical commits
- Prevent data breaches caused by exposed tokens
Key Features of Betterleaks
Betterleaks introduces several features designed to improve secret detection and scanning efficiency.
Token-Based Detection
The tool uses token-efficiency scanning techniques that improve the accuracy of secret detection. This method helps reduce false positives while maintaining a high detection rate.
Custom Detection Rules
Betterleaks supports flexible rule definitions using an expression-based system. This allows developers and security teams to create custom patterns for detecting organization-specific credentials.
High Performance
The tool is written in Go and designed to run quickly even when scanning large repositories. It can analyze files in parallel, making it suitable for large projects and automated pipelines.
Encoded Secret Detection
Betterleaks can identify secrets that are encoded multiple times. This helps detect credentials that may have been intentionally or unintentionally hidden in configuration files.
How to Use Betterleaks
Betterleaks works as a command-line tool, making it easy to integrate into development workflows.
Install the Tool
The tool can be installed using the Go package manager:
go install github.com/betterleaks/betterleaks@latestOnce installed, the command becomes available in the system environment.
Scan a Local Project
Developers can scan a directory containing source code:
betterleaks scan ./project-folderThe tool will analyze files and display any detected secrets.
Scan a Git Repository
Betterleaks can also scan Git repositories and their commit history to detect secrets that may have been added in the past.
betterleaks git https://github.com/example/repositoryThis allows security teams to audit entire projects and identify historical leaks.
Create Custom Detection Rules
Organizations can define custom detection rules to match internal tokens or proprietary authentication formats. These rules help improve detection accuracy for company-specific credentials.
Common Use Cases
Betterleaks can be used in several development and security scenarios.
Local Development Security
Developers can run the tool locally before committing code to ensure no credentials are accidentally included.
CI/CD Pipeline Integration
Security teams can integrate Betterleaks into automated pipelines to scan new commits and pull requests.
Repository Security Audits
Organizations can scan existing repositories to detect leaked secrets that might still be active.
Open-Source Project Protection
Maintainers of open-source projects can use Betterleaks to avoid exposing sensitive configuration data.
Conclusion
Betterleaks is a useful addition to the growing ecosystem of security tools focused on protecting source code repositories. By automatically scanning projects for exposed credentials and offering customizable detection rules, it helps developers identify potential security risks before they become serious vulnerabilities.
In practice, tools like Betterleaks complement other security measures such as Microsoft Patch Tuesday, which ensures that software and systems are regularly updated to fix known vulnerabilities, and Flare VM, a popular Windows-based security distribution used for malware analysis and penetration testing. Together, these tools help security teams maintain safer development environments and reduce the risk of breaches caused by leaked secrets or unpatched systems.
1 thought on “Betterleaks Launches as a New Open-Source Tool for Detecting Leaked Secrets”